
Pen Test Certificate
A penetration test certificate helps you demonstrate to customers, clients, auditors and other stakeholders that independent security testing has been carried out. It provides high-level assurance without sharing the sensitive technical information in a full penetration test report.
At RM Information Security, we provide an assurance certificate as part of our reporting package. Our approach is based on recognised good practice and transparency about the testing undertaken and its outcome, rather than a separate certification scheme with bespoke criteria.
What the Certificate Confirms
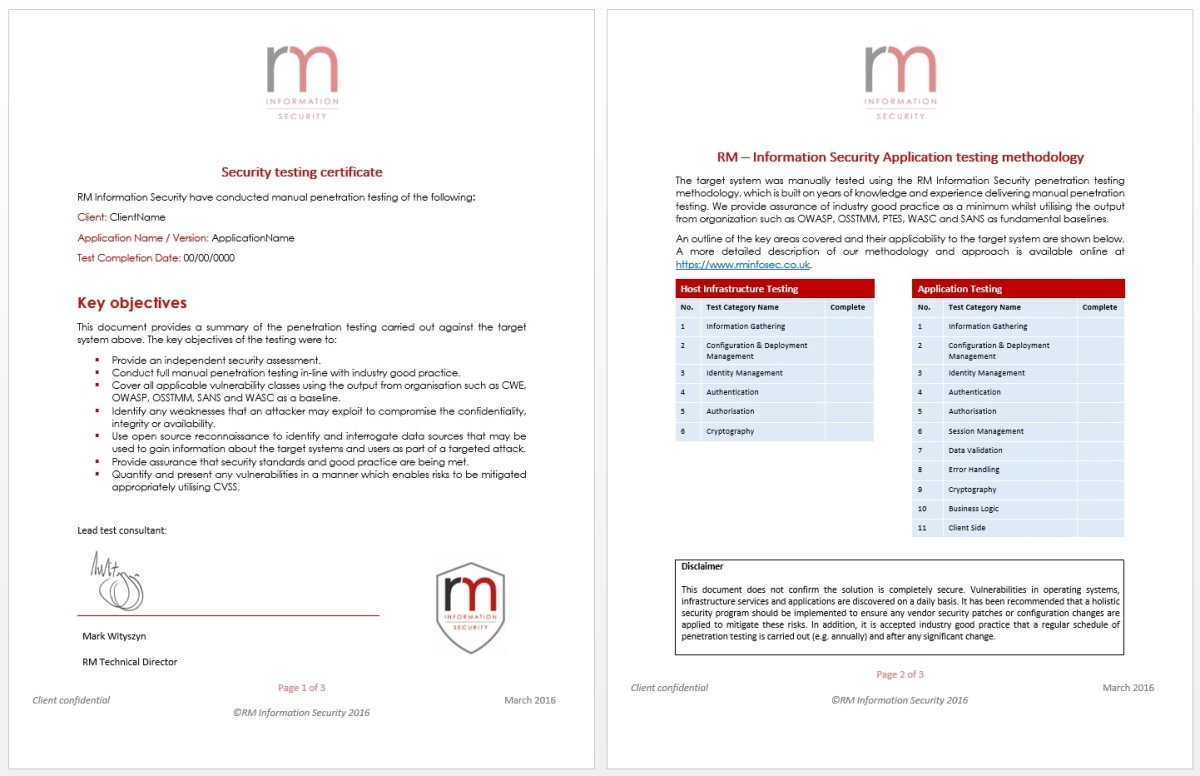
The certificate summarises the assessment completed against the agreed scope. It records the testing undertaken and its outcome at the time of the assessment. It is not a guarantee that a system is free from vulnerabilities or that its security will remain unchanged.
What Information Is Included?
The certificate contains:
- The scope of testing.
- The assessment dates and agreed deliverables.
- A high-level reference to our testing approach.
- A table showing the vulnerabilities covered and their outcome.
Example Pen Test Certificate
Using the Certificate as Evidence
The certificate can help you demonstrate that testing has taken place when sharing the detailed technical report would be inappropriate. The full report may include client data, information about systems outside the recipient’s interest or other sensitive technical details.
The certificate should be read alongside the agreed scope and the penetration test report. It does not replace the detailed findings, risk ratings and remediation recommendations in that report.
If an auditor or client needs further assurance, contact us to discuss their requirements. We can help you understand the information available and how our reporting can support your needs.
Read more about how we work, from initial scoping through to reporting and aftercare.