
Pen Test Report
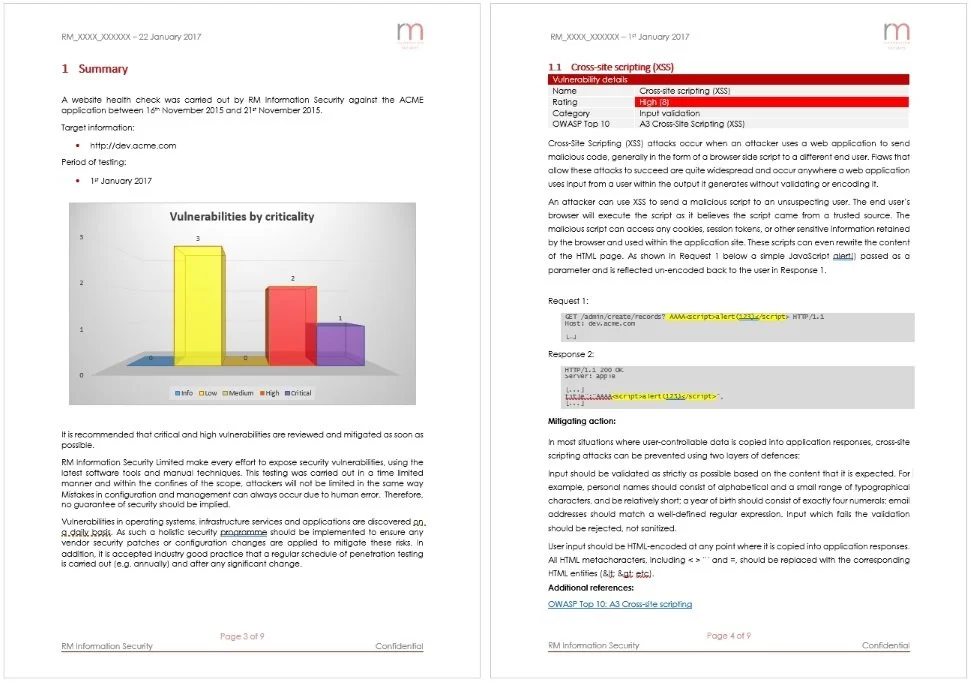
A penetration test is only useful if its findings help you improve security. Our reports communicate the results clearly, from an executive overview for management to the technical evidence developers and system administrators need to address each issue.
Scope and Testing Approach
The introduction sets out the background to the assessment and the agreed scope, summarising the work defined in your proposal. We explain the testing approach and provide the context needed to understand the findings.
Our testing draws on recognised industry guidance, including OWASP and MITRE where applicable. The report makes clear which systems and applications were assessed.
Executive Summary
The executive summary explains the key findings in accessible language, helping management understand the security position and the priorities for improvement. A visual summary of risk supports the written assessment.
Technical Summary
A summary table presents the findings in risk order. Each entry includes a reference, the vulnerability name, its risk rating and a short mitigation summary. Ratings range from Critical and High through Medium and Low to Informational.
We use the Common Vulnerability Scoring System (CVSS) as a basis for assessing technical severity, alongside consultant judgement and the business context. This helps distinguish issues that need urgent attention from lower-risk observations.
Detailed Findings and Evidence
Each detailed finding records the affected systems, risk rating, reference and vulnerability classification, with an OWASP reference where relevant. Technical evidence, code examples and steps to reproduce are included as appropriate so your team can understand the issue and plan a fix.
Practical Remediation Advice
We provide practical recommendations and useful external references for each finding. Where an immediate fix is unavailable, we discuss suitable alternatives or workarounds. Supporting information, such as relevant port-scan output, can be included in appendices.
The value of testing is realised through triage and remediation after the assessment. Our consultants can help you understand the findings and discuss the recommended actions as part of our reporting and aftercare process.
Certificate and Further Assurance
Your reporting package also includes a penetration test certificate, which provides a high-level record of the assessment for customers, clients and auditors without sharing the detailed technical report.
Contact us to discuss your testing requirements and the reporting information your organisation needs.